🛡️ Cyber Security Operations Explained by Kids
Before Anything Goes Wrong
A Security Operations Center, or SOC, is always watching over computers, networks, apps, and data.
A SOC prepares before an attack happens, not just after.
- Systems Get ConnectedComputers, servers, phones, websites, and other devices are connected to the organisation's network.
- Security Tools Start WatchingSpecial security tools look for unusual activity and collect information about what is happening.
- Rules Are SetSecurity teams decide what normal activity looks like and what kinds of events need attention.
- Teams Get ReadySecurity analysts prepare plans for what to do if something suspicious is discovered.
The SOC Is Always Watching
Cybersecurity teams monitor thousands of events that can happen every minute.
The goal is not to watch people. It is to spot activity that could put systems or information at risk.
- Computers 💻Spot strange stuff on people's gadgets!
- Networks 🌐Watch how info travels around the office!
- Accounts 👤Looking for weird logins or account actions!
- Applications 📱Watching big programs and online services!
- Cloud ☁️ Watch systems and information stored in cloud services
When Something Looks Strange
Most unusual activity is not an attack. But when something looks suspicious, the SOC investigates.
An alert is a warning, not automatically proof that an attack has happened.
- Alert Appears 🔔A security system notices something unusual
- Analyst Checks 👀A security analyst examines what happened
- Evidence Is Collected 🔎The team looks at security records and other information
- Risk Is Assessed ⚠️The team decides how serious the event could be
- Action Is Taken 🛡️Security teams follow their response plan
What Is a Security Log?
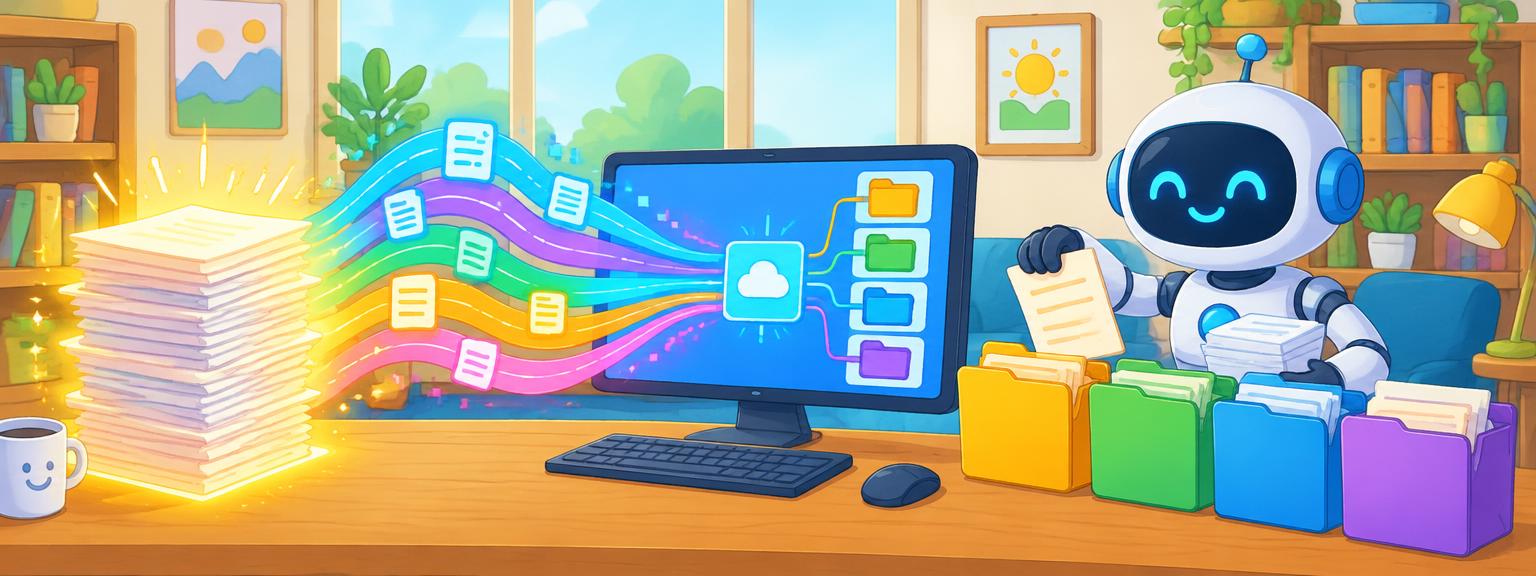
Computers create records of important things that happen. These records can help security teams understand what happened.
Security analysts use these records like clues in a digital investigation.
- LoginRecords when an account signs in
- Network ActivityRecords important connections between systems
- System EventsRecords important changes or activities on a computer
- Security EventsRecords activity detected by security tools
The Security Analyst
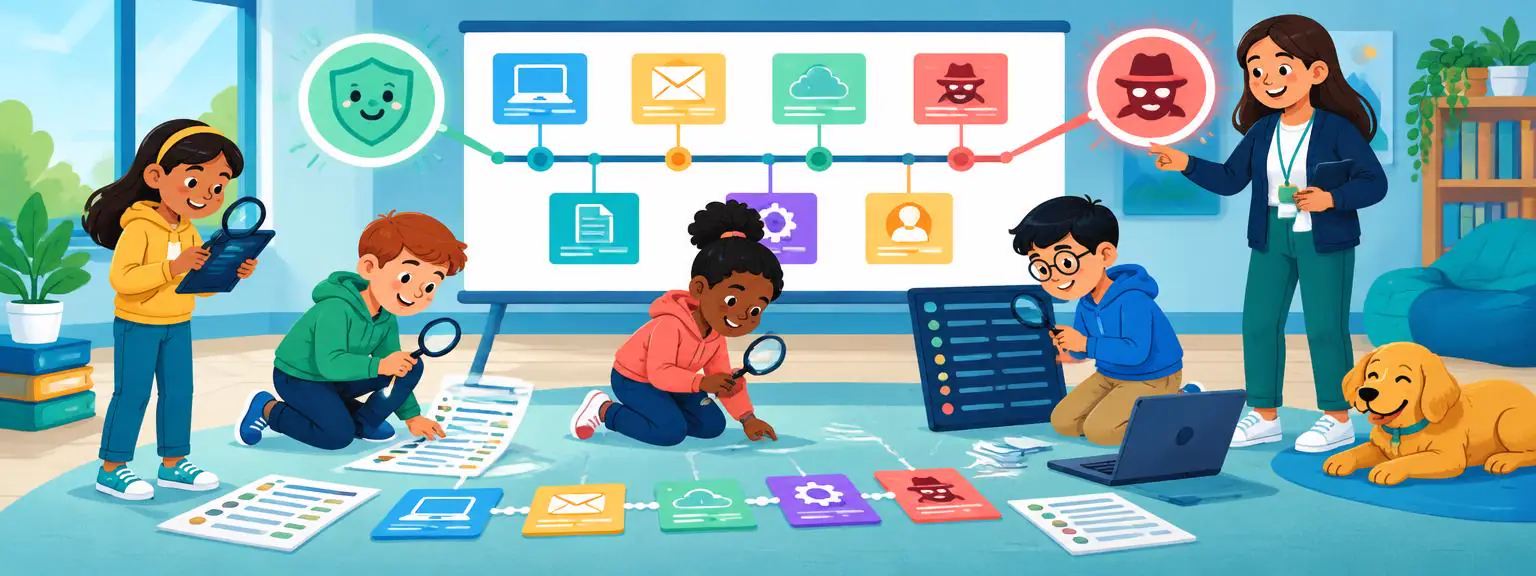
Security analysts are the detectives of a SOC.
A good analyst asks: What happened, and what evidence do we have?
- Watch 👀Keep an eye on alerts!
- Investigate 🔎Figure it out!
- Connect Clues 🧩Look at info from many safety systems!
- Decide ⚖️Does this safety alert need your help now!?
- Respond 🛡️ Help protect systems when a real threat is found
Investigating an Alert
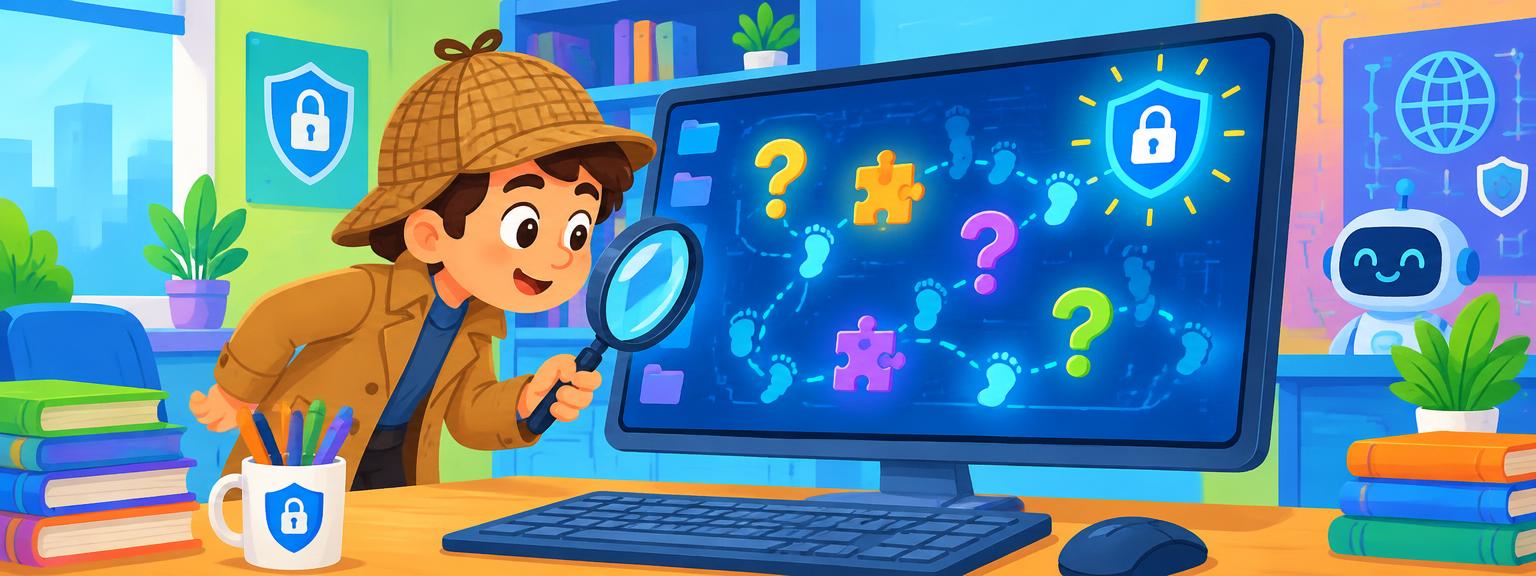
When an alert appears, analysts do not panic. They investigate it step by step.
The investigation turns a confusing alert into a clearer story.
- What Happened? Find out what triggered the alert
- When Did It Happen? Build a timeline of events
- What Was Involved? Affected computer, account, app, or network here!
- Is It Normal? Compare activity with what usually happens. Check now!
- Is It Dangerous? Assess whether there is a genuine security risk
Finding the Bigger Picture
One suspicious event may not mean much by itself. Several events together can reveal a bigger problem.
This is called security investigation.
- Connect EventsSecurity tools combine information from different systems
- Spot PatternsAnalysts look for unusual patterns
- Build a TimelineEvents are placed in the order they happened
- Understand the StoryThe team works out what may have happened
Computers Help the SOC
A SOC can receive far too many alerts for humans to examine every detail manually.
Computers help security teams work faster, while humans make important decisions.
- Automation ⚙️Software can perform routine security tasks automatically
- Detection Rules 📋Security systems look for known warning signs
- AI and Machine Learning 🤖Some systems can help identify unusual patterns
- Alert Prioritisation 🚦Systems can help sort alerts so analysts can focus on important ones
Not Every Alert Is an Attack
SOC teams may receive many warnings every day. Some turn out to be harmless.
The challenge is finding the important alerts among all the noise.
When a Threat Is Confirmed
If an investigation finds a real security incident, the response team begins protecting the organisation.
Cybersecurity is not only about stopping problems. It is also about learning from them.
- Containstop problem spreading; keep it small!
- Protectkeep computers and accounts safe, secure!
- InvestigateFind out what went wrong!
- RecoverMake systems work right again!
- Learnimprove security so a similar incident is less likely again
Protecting Accounts
People's accounts are an important part of cybersecurity.
The safest account has the right protections from the beginning.
- Strong Passwords 🔑Use long, unique passwords
- Multi Factor Authentication 📱Use an additional security check when signing in
- Access Controls 🚪Only give people access to the information they need
- Account Monitoring 👀Watch for unusual sign in activity
Protecting the Network
A network connects computers and devices together, so security teams monitor it carefully.
Think of network security like putting doors between different rooms in a huge building.
- Firewalls 🧱Help control which network connections are allowed
- Network Monitoring 👀Looks for unusual network activity
- Secure Connections 🔒Protect information while it travels between systems
- Segmentation 🧩Separates parts of a network to help limit problems
Protecting the Cloud
Many organisations use cloud services to store information and run applications.
The cloud is still someone else's computer infrastructure. It still needs security.
- Cloud AccountsSecurity teams monitor who can access cloud systems
- Data ProtectionImportant information is protected from unauthorised access
- PermissionsUsers receive only the access they need
- MonitoringSecurity tools watch cloud activity for unusual behaviour
Protecting Devices
Laptops, phones, tablets, and other devices can become targets for cyber threats.
Cybersecurity works best when technology and people work together.
- Updates 🔄Software is kept up to date with security fixes
- Security Software 🛡️Tools can help detect suspicious activity
- Device Monitoring 👀Security teams can monitor important events
- Safe BehaviourPeople learn how to recognise suspicious messages and requests
When a Suspicious Email Is Reported
Imagine someone receives an email that looks suspicious.
Reporting something suspicious can help protect hundreds or thousands of other people.
- Report 📣 The person reports the message to the security team
- Analyse 🔎 Analysts examine the message and its warning signs
- Check 🔗 See if other emails like it show up!
- Protect 🛡️ Keep others safe from bad emails!
- Learn 📚 The team improves future protection
The SOC Team
A SOC is not just one person sitting in front of a computer. It can contain many specialists.
Different specialists work together like a digital emergency team.
- SOC Analyst 👨💻Watches alerts and checks action!
- Incident Responder 🚨Handles real big problems!
- Threat AnalystLooks at scary internet dangers!
- Security EngineerMakes strong computer forts!
- Digital Forensics 🔬 Checks digital clues!
- SOC Manager 🧑💼 Guides the team to success!
SOC Never Sleeps
Many organisations operate around the clock because cyber threats can happen at any time.
This is called 24 hour security monitoring.
- Morning ☀️One team checks overnight activity
- Afternoon 🌤️Analysts investigate alerts and monitor systems
- Evening 🌆Another team takes over monitoring
- Night 🌙Security systems keep watching and analysts respond
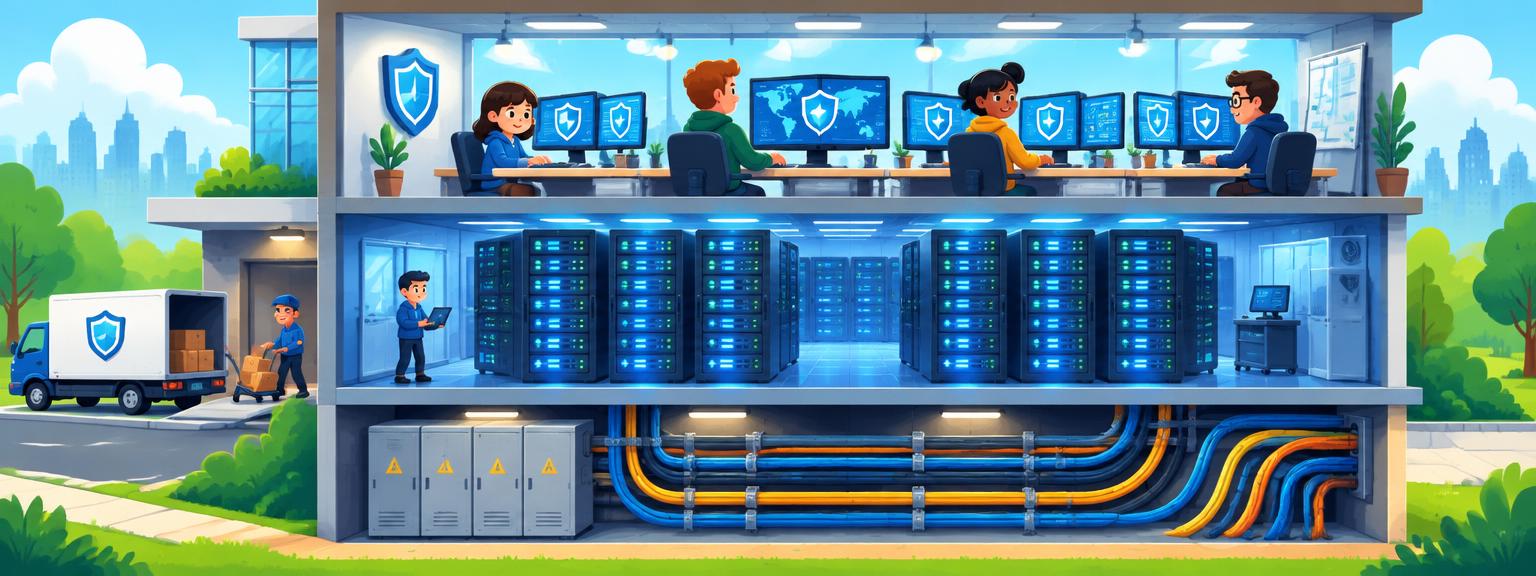
Where Does a SOC Work?
The important part is the security operation, not what the room looks like.
- Internal SOCThe security team works directly for the organisation
- Managed SOCA specialist company provides security monitoring
- Cloud SOCSecurity operations use cloud tools and services
- Global SOC 🌍Teams in different countries work across time zones
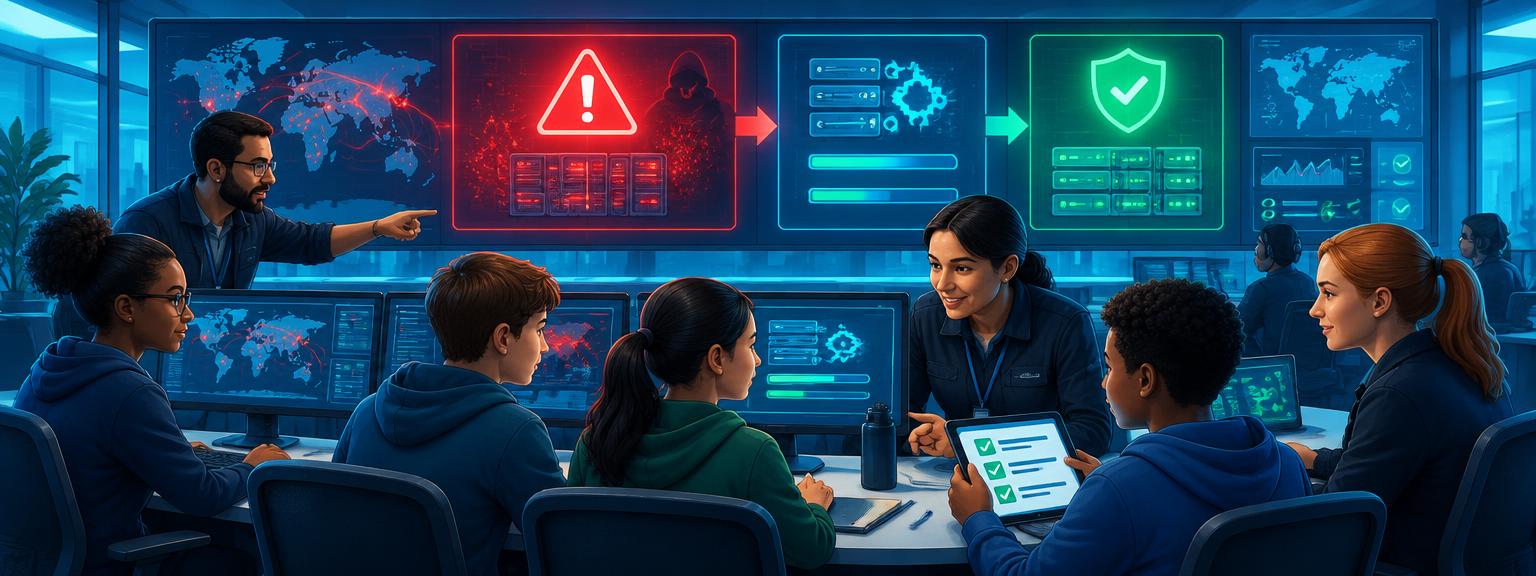
Cybersecurity Emergencies
Some security incidents need an immediate response.
A cyber incident response plan is like an emergency plan for the digital world.
Amazing Cyber SOC Facts
Fast Work!
Security systems can handle lots of info daily!
All Day! !
Many security teams watch systems day and night.
Teamwork
Experts (analysts, engineers) work as a team!
Automation
Computers help sort and check many events fast!
World Wide Web
One event can involve many teams in several countries.
Fact Finders!
Digital detectives use clues to figure out what happened.
Summary
Watching!
An essential part of an effective cybersecurity operation.
Warning!
An essential part of an effective cybersecurity operation.
Find It Out!
An essential part of an effective cybersecurity operation.
Spot It Out!
An essential part of an effective cybersecurity operation.
Fix the Problem!
An essential part of an effective cybersecurity operation.
Stay Safe Online!
An essential part of an effective cybersecurity operation.
Recovery
An essential part of an effective cybersecurity operation.
Learning
An essential part of an effective cybersecurity operation.
Ready for the challenge?
Cyber SOC Mission
You're the on-call analyst at Mango Bank's Security Operations Center. An alert just came in on your screen. Can you figure out what's happening and stop it before it spreads?
Cyber SOC Dictionary
SOC Team!
A team and tools that watch digital systems to keep them safe and sound!
CyberSafe!
Protecting computers, networks, apps, and info from bad guys. Super safe!
Threat
Something that could harm a digital system or info!
Alert
A warning something unusual may have just happened!
Cyber Event!
Cyber event needing a look or fixing, quick!
Alert Hunter!
Person who checks security warnings, wow!
Firewall
A security system that controls network connections
Malware
Software designed to cause harm or steal information
Tricky Phish!
Tricking someone to share info or do something unsafe
Who Are You?
Checking if someone is truly who they say they are
Super Safe Sign In!
Use more than one way to prove it's you when you sign in!
Secret Code Messages!
Scrambling info so only special people can read it! Yes!
What's Up
A list of things that happen on a computer or app!
Look Out!
Info gathered about how a system is working, for fun!
Danger Spot!
Spotting bad or risky stuff, like a sneaky plan!
Just a Joke!
An alarm that seems bad, but it's totally safe!
Threat Intelligence
Information that helps teams understand cyber threats
Incident Response
Managing and responding to a cybersecurity incident
Stop the Spread!
Stopping a computer problem from spreading out
Find the Clues!
Looking at computer clues to see what went on!
Weak Spot!
Something that makes you weak and not safe!
Quick Fix!
An update that fixes problems or weak spots.
Endpoint
A computer, phone, or tablet connected to a network
Network
Connected computers and devices that communicate
SIEM
It gathers and checks computer security clues!
EDR
It watches devices for any odd computer things!
Threat Seeker!
Searches for hidden dangers and bad stuff!
Security Builder!
Builds and improves helpful safety systems!
SOC Manager
The person who coordinates SOC people and processes
You Are Now a Cyber SOC Expert! 🛡️💻
Keep learning, stay curious, and remember: good cybersecurity starts with understanding how to protect the digital world! 🌍🔐
